 55 Park Road,


It’s 6:40 on a Monday morning and your operations manager can’t open the job management system. By 8am the file server is full of encrypted files, a ransom note is sitting on every workstation, and someone in the leadership group is asking whether the insurer will pay. Most of the discussion that follows will be about recovery.
Reporting is the part that gets missed. Depending on your size, your sector and what the attackers touched, the next 72 hours can carry legal obligations to several different Commonwealth bodies. Each has its own trigger, its own form and its own deadline.
This guide sets out what Australian businesses must report after a cyber incident in 2026, who has to report, and how fast. It’s written for business owners, finance managers and operations leads who want the answers in one place before they need them.
General information only, current as of October 2026. This is not legal advice, and your lawyer and insurer should be involved in any live incident.
One Ransomware Attack Can Start Several Reporting Clocks at Once
Australian cyber incident reporting is a set of overlapping obligations. They were built at different times, for different purposes, and are administered by different agencies. The ones most likely to matter are:
| Obligation | Who it applies to | Report to | Deadline |
| Ransomware and cyber extortion payment reporting (Cyber Security Act 2024) | Businesses with annual turnover over $3 million in the previous financial year, plus responsible entities for critical infrastructure assets | Australian Signals Directorate (ASD), via cyber.gov.au | 72 hours after the payment is made, or after you become aware it was made |
| Notifiable Data Breaches scheme (Privacy Act 1988) | Organisations covered by the Privacy Act, including most businesses over $3 million turnover, all private health service providers, and certain others regardless of size | Office of the Australian Information Commissioner (OAIC) and affected individuals | Assess within 30 days; notify as soon as practicable |
| Mandatory cyber incident reporting (Security of Critical Infrastructure Act 2018) | Responsible entities for critical infrastructure assets | ASD’s Australian Cyber Security Centre (ACSC) | 12 hours or 72 hours, depending on impact |
| Prudential Standard CPS 234 | APRA-regulated entities | APRA | 72 hours for material information security incidents |
For an ordinary mid-sized Sydney business, the Monday morning scenario above could trigger the first two obligations. For a superannuation administrator, an insurer or a utility, it could trigger all four.
Paying a Ransom Now Means Telling the Government Within 72 Hours
Part 3 of the Cyber Security Act 2024 created Australia’s mandatory ransomware payment reporting regime, which commenced on 30 May 2025. If your business is a “reporting business entity” and a ransomware or cyber extortion payment is made in connection with an incident affecting you, you must report it to ASD within 72 hours. The clock starts when the payment is made, or when you become aware that someone made it on your behalf.
Several details catch businesses out:
- The turnover test looks backwards. The $3 million threshold applies to your previous financial year. A business that grew past it last year is already covered, whether or not anyone has noticed.
- Payments made on your behalf still count. If your insurer, an incident response firm or a specialist negotiator pays the ransom, the reporting obligation stays with you.
- The payment doesn’t have to be money. Non-monetary benefits given to the attacker are also covered.
- There is no minimum amount. A small ransom carries the same obligation as a large one.
- No payment means no ransomware payment report. If you refuse to pay, this particular obligation doesn’t arise, although your other obligations may still apply.
The report covers the incident and its impact on your business, the demand, the payment itself (amount and method), your communications with the attacker, and any third party involved in paying. The Department of Home Affairs’ factsheet on ransomware payment reporting sets out these requirements and links to the reporting form.
Home Affairs ran an “education first” phase until 31 December 2025, taking action only for egregious non-compliance. Since 1 January 2026 it has operated a compliance and enforcement approach. A failure to report carries a civil penalty of 60 penalty units. The Commonwealth penalty unit was indexed to $364 on 1 July 2026, so that is now $21,840 per contravention. That figure is small next to a typical ransom. The larger risk is having an unreported payment come to light later, during an insurance claim or a privacy investigation.
The Act includes protections designed to encourage honest reporting. Information in a ransomware payment report generally can’t be used as evidence against the reporting business in civil or criminal proceedings, and Home Affairs has said that reporting does not waive legal professional privilege.
Two things the regime does not do:
- It does not make paying a ransom illegal. Separately, though, payments to sanctioned individuals or groups can breach Australian sanctions law.
- It does not satisfy your privacy obligations. A ransomware payment report and a data breach notification go to different agencies, under different laws, for different purposes.
Under the Privacy Act, the Trigger Is Likely Serious Harm, Not Certainty
The Notifiable Data Breaches (NDB) scheme sits in Part IIIC of the Privacy Act 1988. It applies to organisations covered by the Privacy Act, which the Act calls “APP entities”.
Many businesses assume the small business exemption covers them. The exemption has significant gaps:
- Health services. Private health service providers are covered regardless of turnover. That includes GPs, dentists, physiotherapists, psychologists and allied health practices.
- Data-related businesses. Businesses that trade in personal information are covered. So are credit reporting bodies and businesses handling tax file numbers, for that information.
- AML/CTF reporting entities (new from 1 July 2026). Businesses brought into the anti-money laundering regime are now covered for personal information they handle for AML/CTF purposes. This includes many law firms, accounting practices and real estate agencies.
A breach is an “eligible data breach” when all three of these conditions are met:
- Personal information has been accessed or disclosed without authorisation, or lost in circumstances where that is likely.
- The breach is likely to result in serious harm to one or more individuals.
- You haven’t been able to prevent that likely harm through remedial action.
If you suspect an eligible breach, you must take all reasonable steps to complete an assessment within 30 calendar days. The OAIC treats 30 days as an outer limit, not a target. Once you have reasonable grounds to believe an eligible breach has occurred, you must notify the OAIC and the affected individuals as soon as practicable. The OAIC’s quick reference guide for responding to data breaches walks through the assessment and the notification form.
Ransomware makes this harder. Most modern ransomware groups steal data before they encrypt it, then threaten to publish it. Concluding that files were “encrypted but not taken” requires evidence, such as firewall logs, endpoint telemetry and the audit records produced by a properly configured Microsoft 365 security environment. Without that evidence, you often can’t rule out unauthorised access, and the assessment tends to lean towards notification.
Notifications are increasing. The OAIC received 1,205 data breach notifications in 2025, the highest annual total since the scheme began in 2018. Of those, 716 were attributed to malicious or criminal activity. Health service providers were the most affected sector, accounting for 19% of notifications.
Critical Infrastructure and Financial Services Run on Tighter Clocks
Critical infrastructure
If your business is a responsible entity for a critical infrastructure asset under the SOCI Act, two deadlines apply, both counted from when you become aware of the incident:
- 12 hours for an incident having a significant impact on the availability of the asset.
- 72 hours for an incident having, or likely to have, a relevant impact on its integrity, reliability or confidentiality.
These reports go to ASD’s ACSC through its cyber security incident reporting page. If you report verbally, you must follow up with a written record within 84 hours for a critical incident, or 48 hours for any other incident. SOCI responsible entities are also covered by the ransomware payment regime regardless of turnover.
APRA-regulated entities
Banks, insurers, superannuation trustees and private health insurers must notify APRA under CPS 234:
- 72 hours after becoming aware of a material information security incident.
- 10 business days after becoming aware of a material control weakness that can’t be fixed promptly.
An incident at one of your service providers that affects your information assets is still your incident under CPS 234.
Listed companies and suppliers
Listed companies should also consider their ASX continuous disclosure obligations if an incident is material to the share price.
Many Sydney businesses are not SOCI or APRA entities themselves but supply organisations that are. Supplier contracts with these organisations frequently require notification within 24 hours or less. Check what you have signed.
The 30-Day Privacy Window Is Set to Shrink to 72 Hours
On 31 August 2026, the Attorney-General’s Department released an exposure draft of the Privacy Amendment (Personal Data Protection) Bill 2026, the second tranche of Privacy Act reform. Under the draft:
- The current 30-day assessment window would be removed.
- Once an organisation becomes aware of reasonable grounds to believe an eligible data breach has occurred, it would have 72 hours to give the Information Commissioner a statement.
- An incomplete statement would be allowed where full details aren’t yet available.
- Missing the deadline could result in an infringement notice or a compliance notice.
Submissions closed on 18 September 2026. The draft does not remove the small business exemption. Law firm Herbert Smith Freehills Kramer’s summary of the draft is a useful overview of what else is proposed.
This is not yet law, and the detail may change before a bill reaches Parliament. The direction is clear, though: almost every major Australian incident reporting deadline is converging on 72 hours. Planning around 72 hours now is better than redesigning your response process later.
Meeting Any of These Deadlines Depends on Decisions Made Before the Incident
Seventy-two hours disappears quickly when the attack starts on a Friday night. The businesses that report accurately and on time have usually settled the following in advance:
- Which regimes apply to you. Check your turnover for the last financial year, whether you provide health services, whether you are an AML/CTF reporting entity, whether you are covered by SOCI, APRA or ASX rules, and what your client contracts require.
- Who decides and who lodges each report. Name a decision-maker for each report, with a deputy for weekends and holidays.
- Evidence that survives the attack. Make sure Microsoft 365 audit logging is enabled with adequate retention, and keep endpoint detection and firewall logs. Without logs, you can’t determine what data was taken.
- Recovery that doesn’t depend on the attacker. Keep backups where attackers can’t reach them. Offline or immutable cloud backup and a tested disaster recovery plan give you a real alternative to paying, which means there may be no ransom payment to report.
- A pre-agreed position with your insurer and lawyer. Settle who can authorise a ransom payment, who makes it, and who reports it.
- Draft templates. Prepare drafts of the OAIC statement, the ransomware payment report fields and customer notifications, so you aren’t writing them from scratch at 2am.
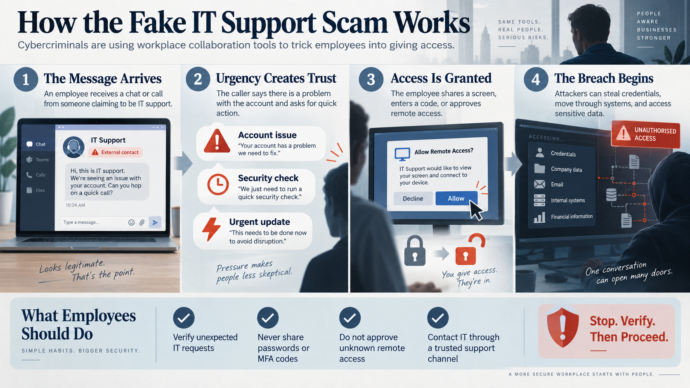
- A rehearsal, and a test of your defences. Run a tabletop exercise based on a weekend ransomware scenario at least once a year as part of your business continuity planning. Regular penetration testing shows you where an attacker would get in before one does. Since phishing and credential theft are common entry points, review your email security at the same time.
Most of this work is technical preparation that shows its value under legal pressure. The reporting decisions belong to you and your legal advisers. Having the forensic timeline, log evidence and scoping ready when they ask is what makes those decisions possible within the deadline.
Businesses without an internal IT team can build this readiness into ongoing managed IT services. Businesses that do have in-house IT can use a co-managed IT arrangement to add after-hours monitoring and incident support.
For more on how Sydney Technology Solutions approaches cyber security and incident readiness for Sydney businesses, see our Cyber Security Services in Sydney page, or contact our team to talk through your reporting obligations and response plan.